Anonymous Verified Buyer
" Very responsive and helpful, competitive pricing. Good source! "
July 2025
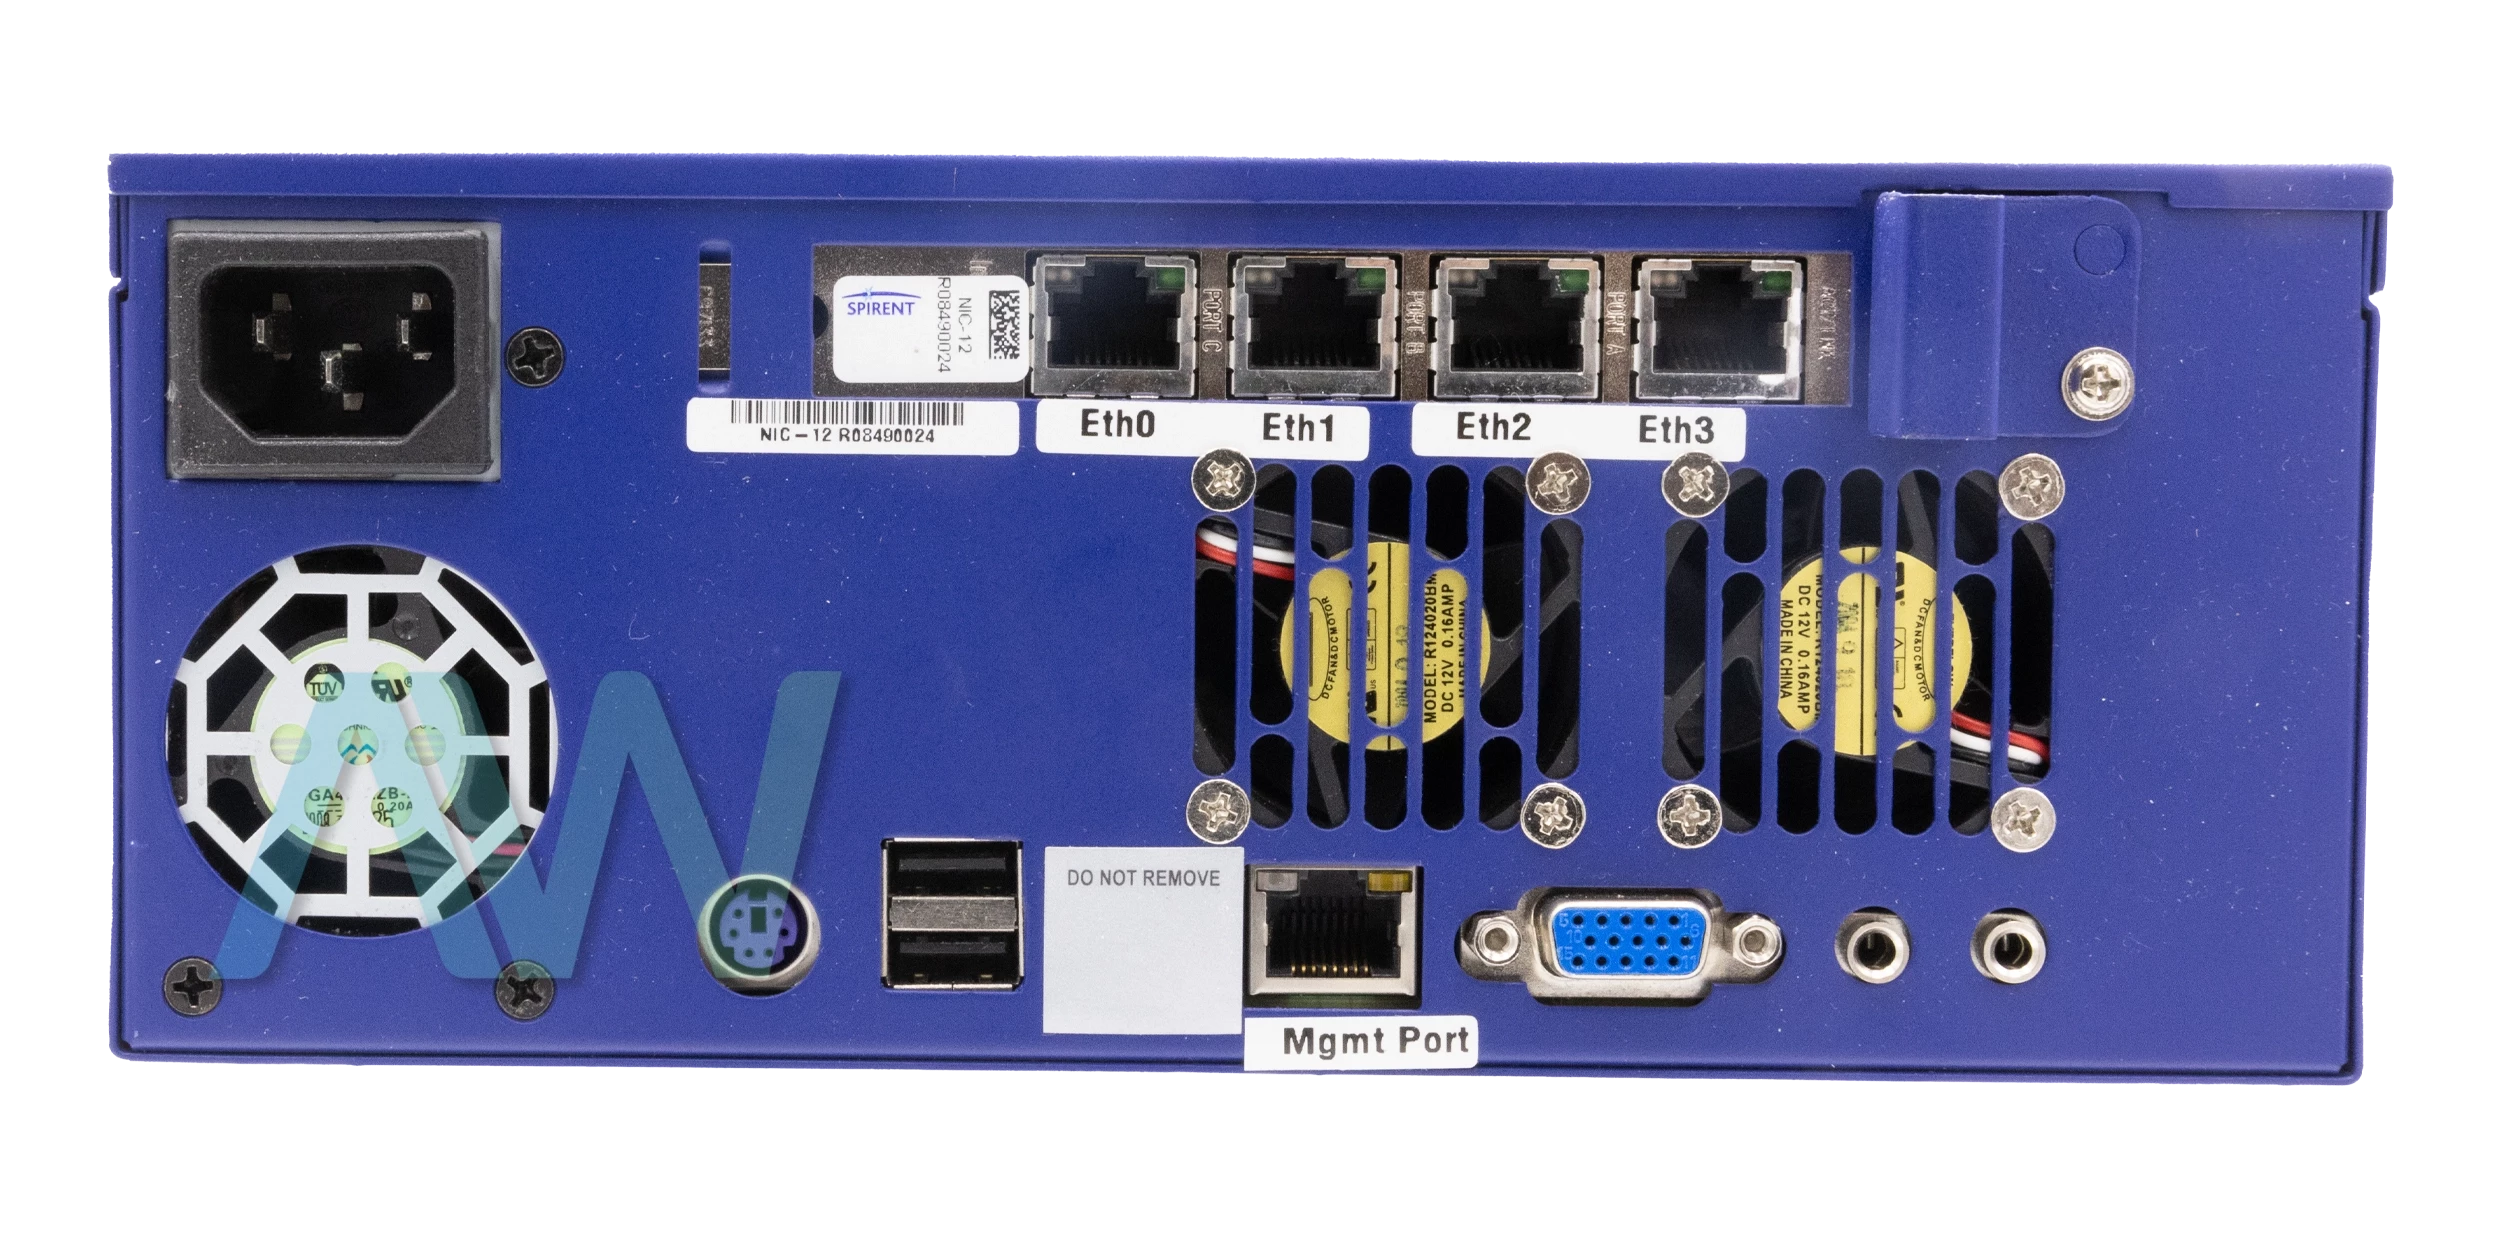
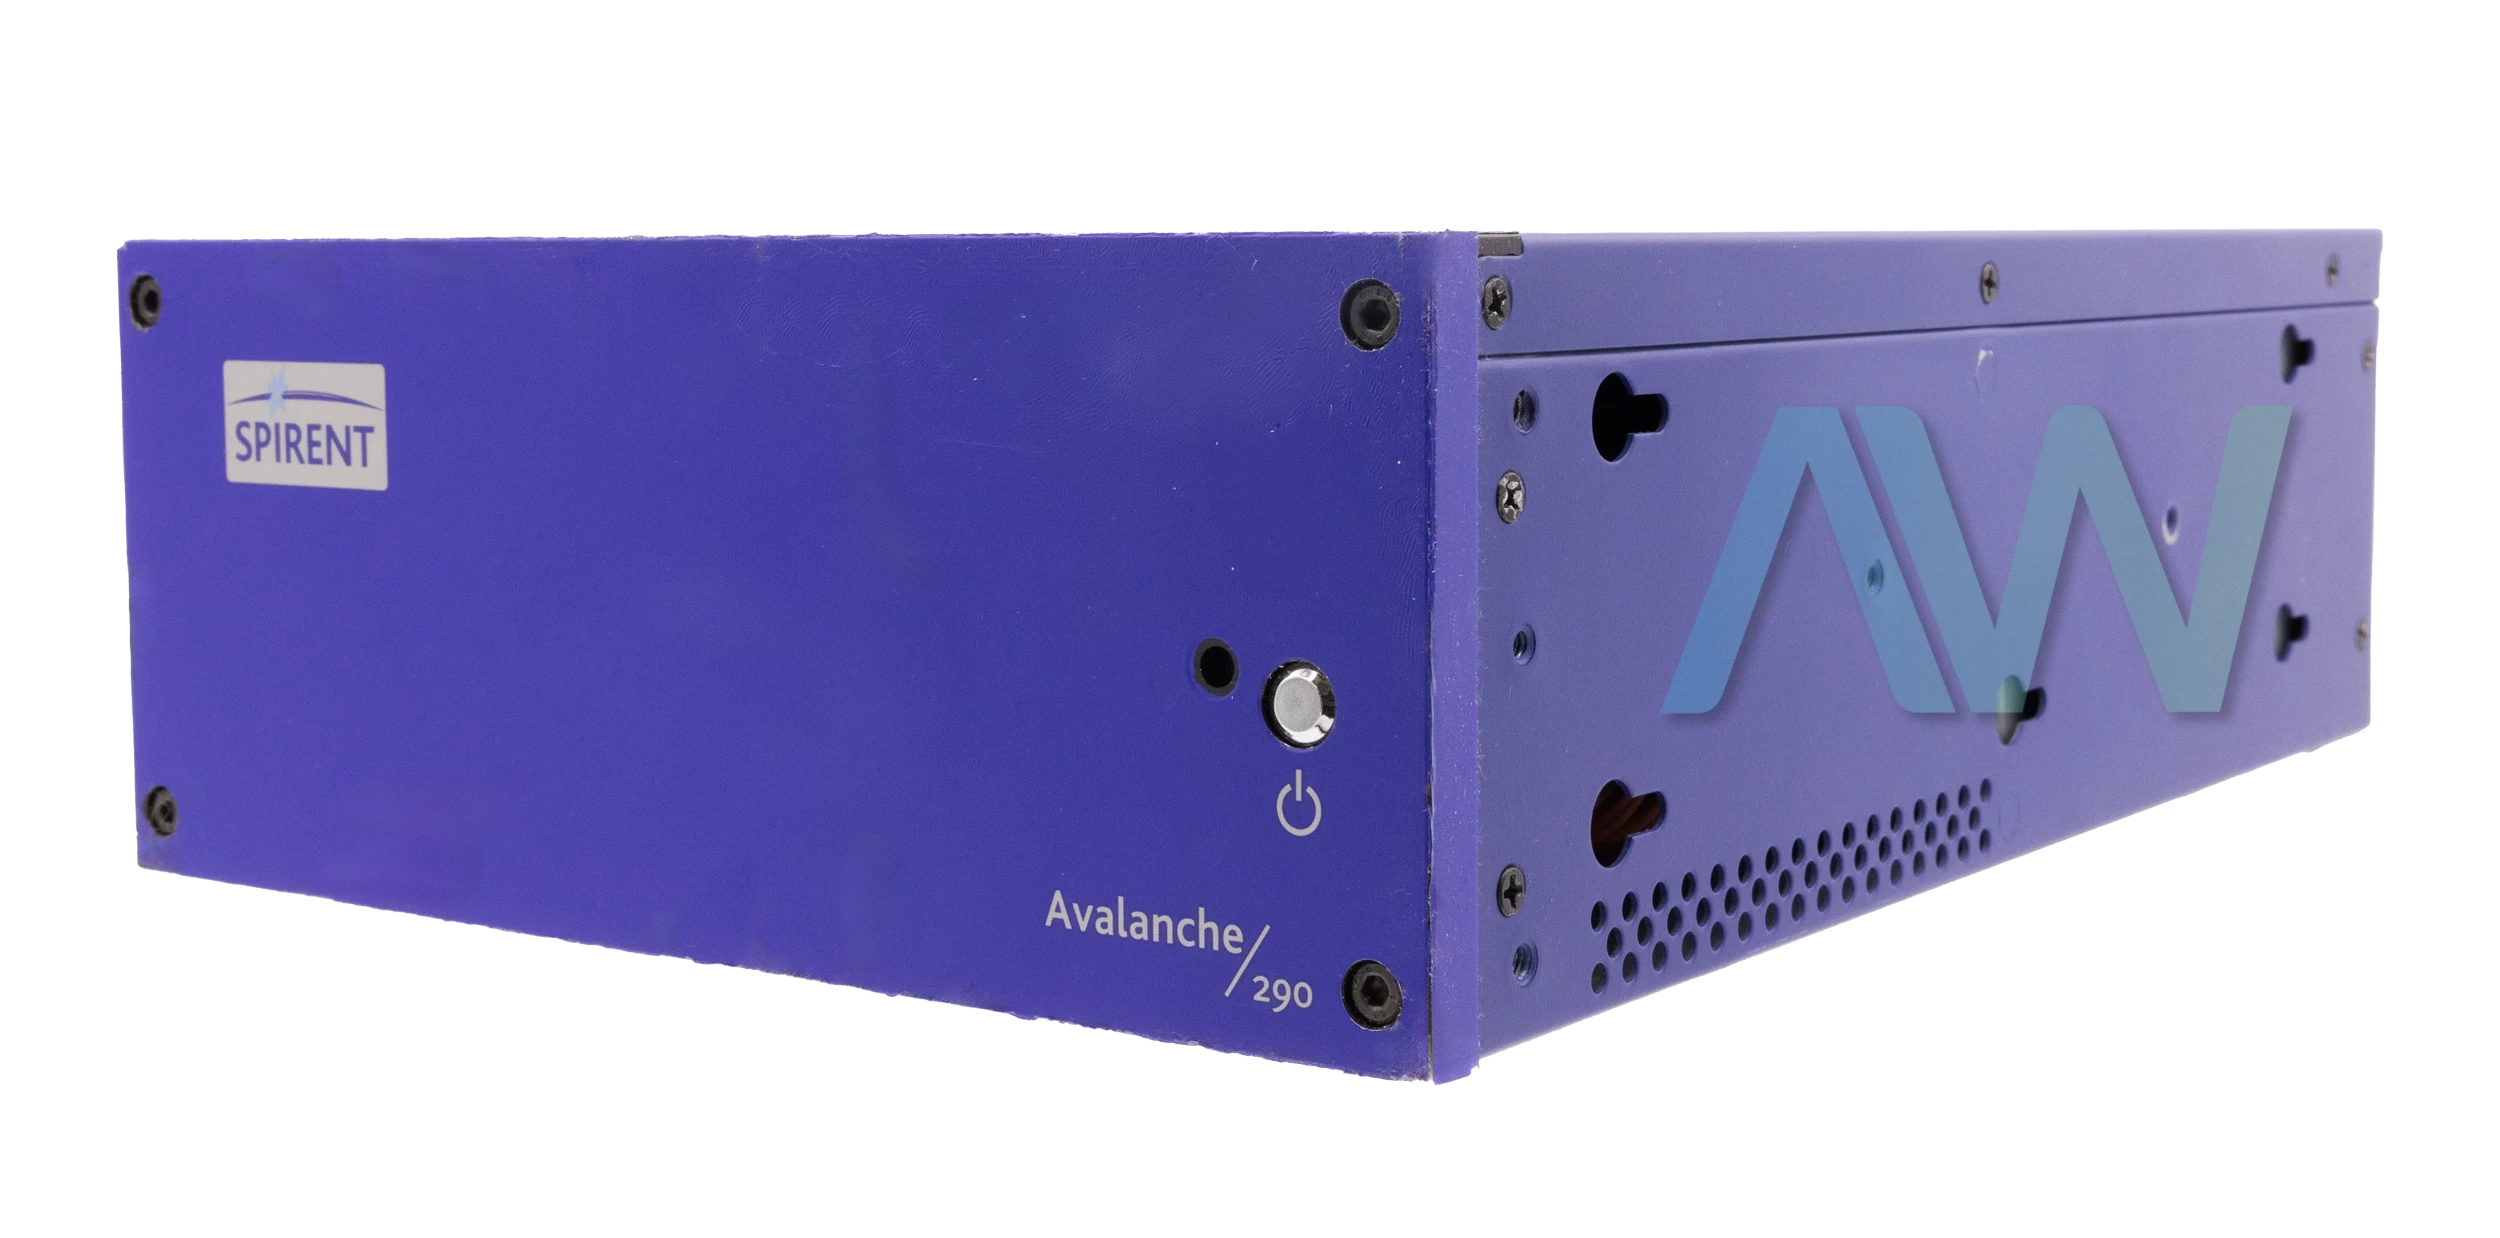
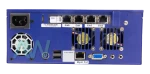
Spirent CEE-290, 4 Ethernet Ports, Scalable Application Protocol Emulation
Actual item may vary if no part number is provided on quote request.


✔ 2 Year Warranty Included
✔ Free Domestic Ground Shipping
✔ NIST Calibration Available
Anonymous Verified Buyer
" Very responsive and helpful, competitive pricing. Good source! "
July 2025
Andrew Gar**** Verified Buyer
" Amazing to work with and had my order within 1 week after purchasing with all NI certs and data that were needed. "
March 2025
Said Sai**** Verified Buyer
" Competent contact for highly specialized components. The support team is very knowledgeable. Many thanks for the help and the fast shipping! "
January 2025
Bob C**** Verified Buyer
" Jason was able to get our emergency situation taken care of quickly and professionally. "
May 2025
Gregg Flecki**** Verified Buyer
" Great service and great products. This is my 2nd time using Apex Waves, truly impressed. "
January 2025

Carol Zimme**** Verified Buyer
" Very responsive and helpful, competitive pricing. Good source! "
July 2025
Andrew Gar**** Verified Buyer
" Amazing to work with and had my order within 1 week after purchasing with all NI certs and data that were needed. "
March 2025
Said Sai**** Verified Buyer
" Competent contact for highly specialized components. The support team is very knowledgeable. Many thanks for the help and the fast shipping! "
January 2025
Bob C**** Verified Buyer
" Jason was able to get our emergency situation taken care of quickly and professionally. "
May 2025
Gregg Flecki**** Verified Buyer
" Great service and great products. This is my 2nd time using Apex Waves, truly impressed. "
January 2025
Spirent CEE-290 Scalable Application Protocol Emulation
The Spirent CEE-290 is a 4-port Scalable Application Protocol Emulation appliance, designed for rigorous cybersecurity and network application testing. CEE-290 is acclaimed for its high efficiency in Layer 4-7 testing, thus empowering users to test network resiliency under conditions of heavy load with simulated threats and to emulate large-scale, mixed-traffic environments accurately. Its core functionality enables comprehensive tests of vulnerabilities with simulated behavior in a controlled way, providing critical insights into the behavior and performance of network defenses exposed to both standard and malicious traffic.
One major differentiator in its favor is that the Spirent CEE-290 packs in the ThreatEx solution for emulating complex, voluminous cyberattacks-from DDoS assaults to application-layer threats, worms, and advanced persistent malware. Moreover, the device enables a wide array of out-of-the-box threat scenarios and user-configurable attack templates via the Spirent Avalanche Attack Knowledge Base that is continuously updated with the latest threat definitions. It facilitates zero-day vulnerability testing by network security professionals and tailoring of threat profiles according to their particular security needs. Up-to-date threat data allows users to adapt defenses against the evolving security landscape effectively.
CEE-290 is part of the greater Avalanche system from Spirent, through which an intuitive graphical interface easily configures test parameters, attack vectors, and statistical monitoring. The system merges normalized user traffic with attack traffic so as to highlight key vulnerabilities and network response times. Due to this dual approach, the reliability of firewalls, VPNs, and intrusion detection systems increases, and IT personnel will know exactly how to find and fix weaknesses in the network defenses under real-world conditions.
The CEE-290 is designed to scale up and support multi-platform environments, even those hosted on cloud-based infrastructures. Spirent's TCL API fully automates test scenarios, further enhancing repeatability and saving time in repeated vulnerability assessments. This becomes an important feature for enterprises that require ongoing security evaluation and continuous compliance validation.
| Model | CEE-290 |
|---|---|
| Port Configuration | 4-Port Gigabit Ethernet (GigE) |
| Testing Layer | Layer 4-7 application testing |
| Bandwidth | Up to 2 Gbps throughput |
| Traffic Emulation | Emulates standard and malicious traffic flows |
| Attack Simulation | DDoS, port scans, malware, and fragmented attacks |
| Threat Database | Continuously updated with latest threat definitions |
| Automation API | TCL API for automated testing |
| Custom Attack Profiles | Built-in designer for custom threat simulation |
| Deployment | Supports both virtual and physical environments |
Associated part numbers for CEE-290:
Delivery:
Eligible returns may be accepted within 30 days at Apex Waves’ discretion. A 25% restocking fee applies; non-refundable and built-to-order products are excluded.
Payment:



Receive Price & Availability Today!
Ask About Our Tiered Calibration Levels
Option & Modules:
Confirm Your Requirements or Versions
Cost & Lead Time Available Upon Request for Service
Repair Evaluation: $150
Common Typos: